Search
Table of contents
- What Is Quantum Security? Preparing for the Post-Quantum Era
-
What Is a Cryptography Bill of Materials (CBOM)?
- Why Is a CBOM Important?
- Benefits of a CBOM
- How Does a CBOM Work?
- Example: Using a CBOM to Identify Cryptographic Risk
- How Does a CBOM Support Post-Quantum Cryptography Migration?
- Best Practices for CBOM Management
- Threat Intelligence: How Cryptographic Threats Affect CBOM Priorities
- How to Implement a CBOM
- Challenges of CBOM Management
- Future Trends in CBOM Management
- CBOM FAQs
-
Harvest Now, Decrypt Later: Quantum Security Risk
- How Does a Harvest Now, Decrypt Later Attack Work?
- Unit 42 Perspective: Data Theft Is Already Moving Faster
- Why HNDL Matters Before Quantum Computers Exist
- Which Organizations and Data Are Most Exposed?
- How Attackers Exploit the Window Before PQC
- How HNDL Connects to Q-Day
- How to Prepare for Harvest-Now, Decrypt-Later Attacks
- How HNDL Fits Into a Broader Quantum Security Strategy
- HNDL FAQs
- Quantum Readiness: How to Prepare for Post-Quantum Security
- NIST PQC Migration Strategies: Steps, Standards & Tips
-
What Is Post-Quantum Cryptography (PQC)? A Complete Guide
- Post-Quantum Cryptography Explained
- The Quantum Threat to Modern Encryption
- How Post-Quantum Cryptography Works
- Standardized Algorithms: NIST FIPS 203, 204, and 205
- Preparing for the Post-Quantum Transition
- PQC Challenges and Implementation Pitfalls
- How Can Organizations Prepare for PQC?
- Post-Quantum Cryptography FAQs
-
What Are NIST PQC Standards?
- NIST PQC Standards Explained
- The Urgency of Quantum-Resistant Cryptography
- What Is the Timeline for PQC Adoption?
- Core NIST PQC Standards and Finalized Algorithms
- What PQC Standards Exist Today?
- How Do Global PQC Standards and Policies Differ?
- What Is Hybrid Cryptography?
- How NIST PQC Standards Differ from Classical Encryption
- Strategic Migration: Implementing NIST PQC Standards
- Unit 42 Insights: The Evolving Threat Landscape
- Overcoming PQC Implementation Challenges
- PQC Readiness: What to Do Now
- Quantum security FAQs
-
8 Quantum Computing Cybersecurity Risks + How to Prepare
- What Are Quantum Computing Cybersecurity Risks?
- Why Quantum Computing Threatens Cybersecurity
- 1. Breaking Public-Key Encryption
- 2. Harvest-Now, Decrypt-Later Attacks
- 3. Forgery of Digital Signatures
- 4. Compromise of Secure Boot Processes
- 5. Vulnerability of Financial Transactions and Ledgers
- 6. Decryption of Historical Data Backups
- 7. Identity and Access Management Failure
- 8. Obsolescence of Legacy IoT and Embedded Systems
- Quantum Threat and Readiness Timeline
- How Organizations Can Prepare For Quantum Cybersecurity Risks
- Quantum Computing Cybersecurity Risk Examples
- What changed recently in post-quantum cybersecurity?
- Quantum Computing Cybersecurity Risks FAQs
What Is Q-Day?
4 min. read
Table of contents
Q-Day is the point when quantum computers become powerful enough to break today’s widely used public-key cryptography. It is not a specific calendar date. It is a capability milestone that would allow a cryptographically relevant quantum computer, or CRQC, to break algorithms such as RSA and elliptic-curve cryptography.
Most experts expect Q-Day to occur in the 2030s or later, but the exact timing is uncertain. The larger cybersecurity risk begins before Q-Day, as attackers can steal encrypted data today and decrypt it later when quantum capabilities mature.
Key Points
-
Q-Day is a cryptographic milestone: It marks the point when quantum computers can break public-key encryption used to secure digital communications, identities, and transactions. -
Q-Day is not expected tomorrow: Most expert estimates place cryptographically relevant quantum computers in the 2030s or later, though timelines vary. -
The risk starts before Q-Day: Harvest-now, decrypt-later attacks allow adversaries to collect encrypted data now and decrypt it in the future. -
Public-key cryptography is most exposed: RSA, elliptic-curve cryptography, public key infrastructure, certificates, and digital signatures face the greatest quantum risk. -
Post-quantum migration must begin now: Organizations need cryptographic visibility, crypto-agility, vendor readiness, and migration roadmaps before quantum risk becomes urgent.
Why Experts Disagree About When Q-Day Will Happen
"There is large variability among the opinions of the experts: some lean towards optimism, while others are more cautious about the pace at which quantum computers will be developed."
- Global Risk Institute, Quantum Threat Timeline Report 2024
Hardware
Different quantum computing models use different physical approaches, including superconducting circuits, trapped ions, and photonic systems. Each approach has trade-offs. Some are easier to scale but harder to stabilize. Others may be more accurate but more difficult to manufacture at large scale.
Error Correction
Error correction is another major barrier.
Quantum bits, or qubits, are fragile. They can lose coherence quickly, which makes long calculations difficult. Breaking modern public-key cryptography would require large numbers of fault-tolerant logical qubits. That likely means millions of physical qubits working together to create a smaller number of reliable logical qubits.
Algorithmic Efficiency
Algorithmic progress also adds uncertainty. Breakthroughs in quantum algorithms could accelerate the timeline, while improvements in classical defenses and post-quantum standards could reduce risk.
In practical terms, experts disagree because they are assessing different breakthroughs. Some focus on physics. Others focus on engineering, error correction, or cryptographic math.
The exact date matters less than the preparation window. For security teams, the risk begins long before Q-Day because sensitive data can be stolen today and decrypted later.
What Would Happen If Q-Day Arrived Tomorrow?
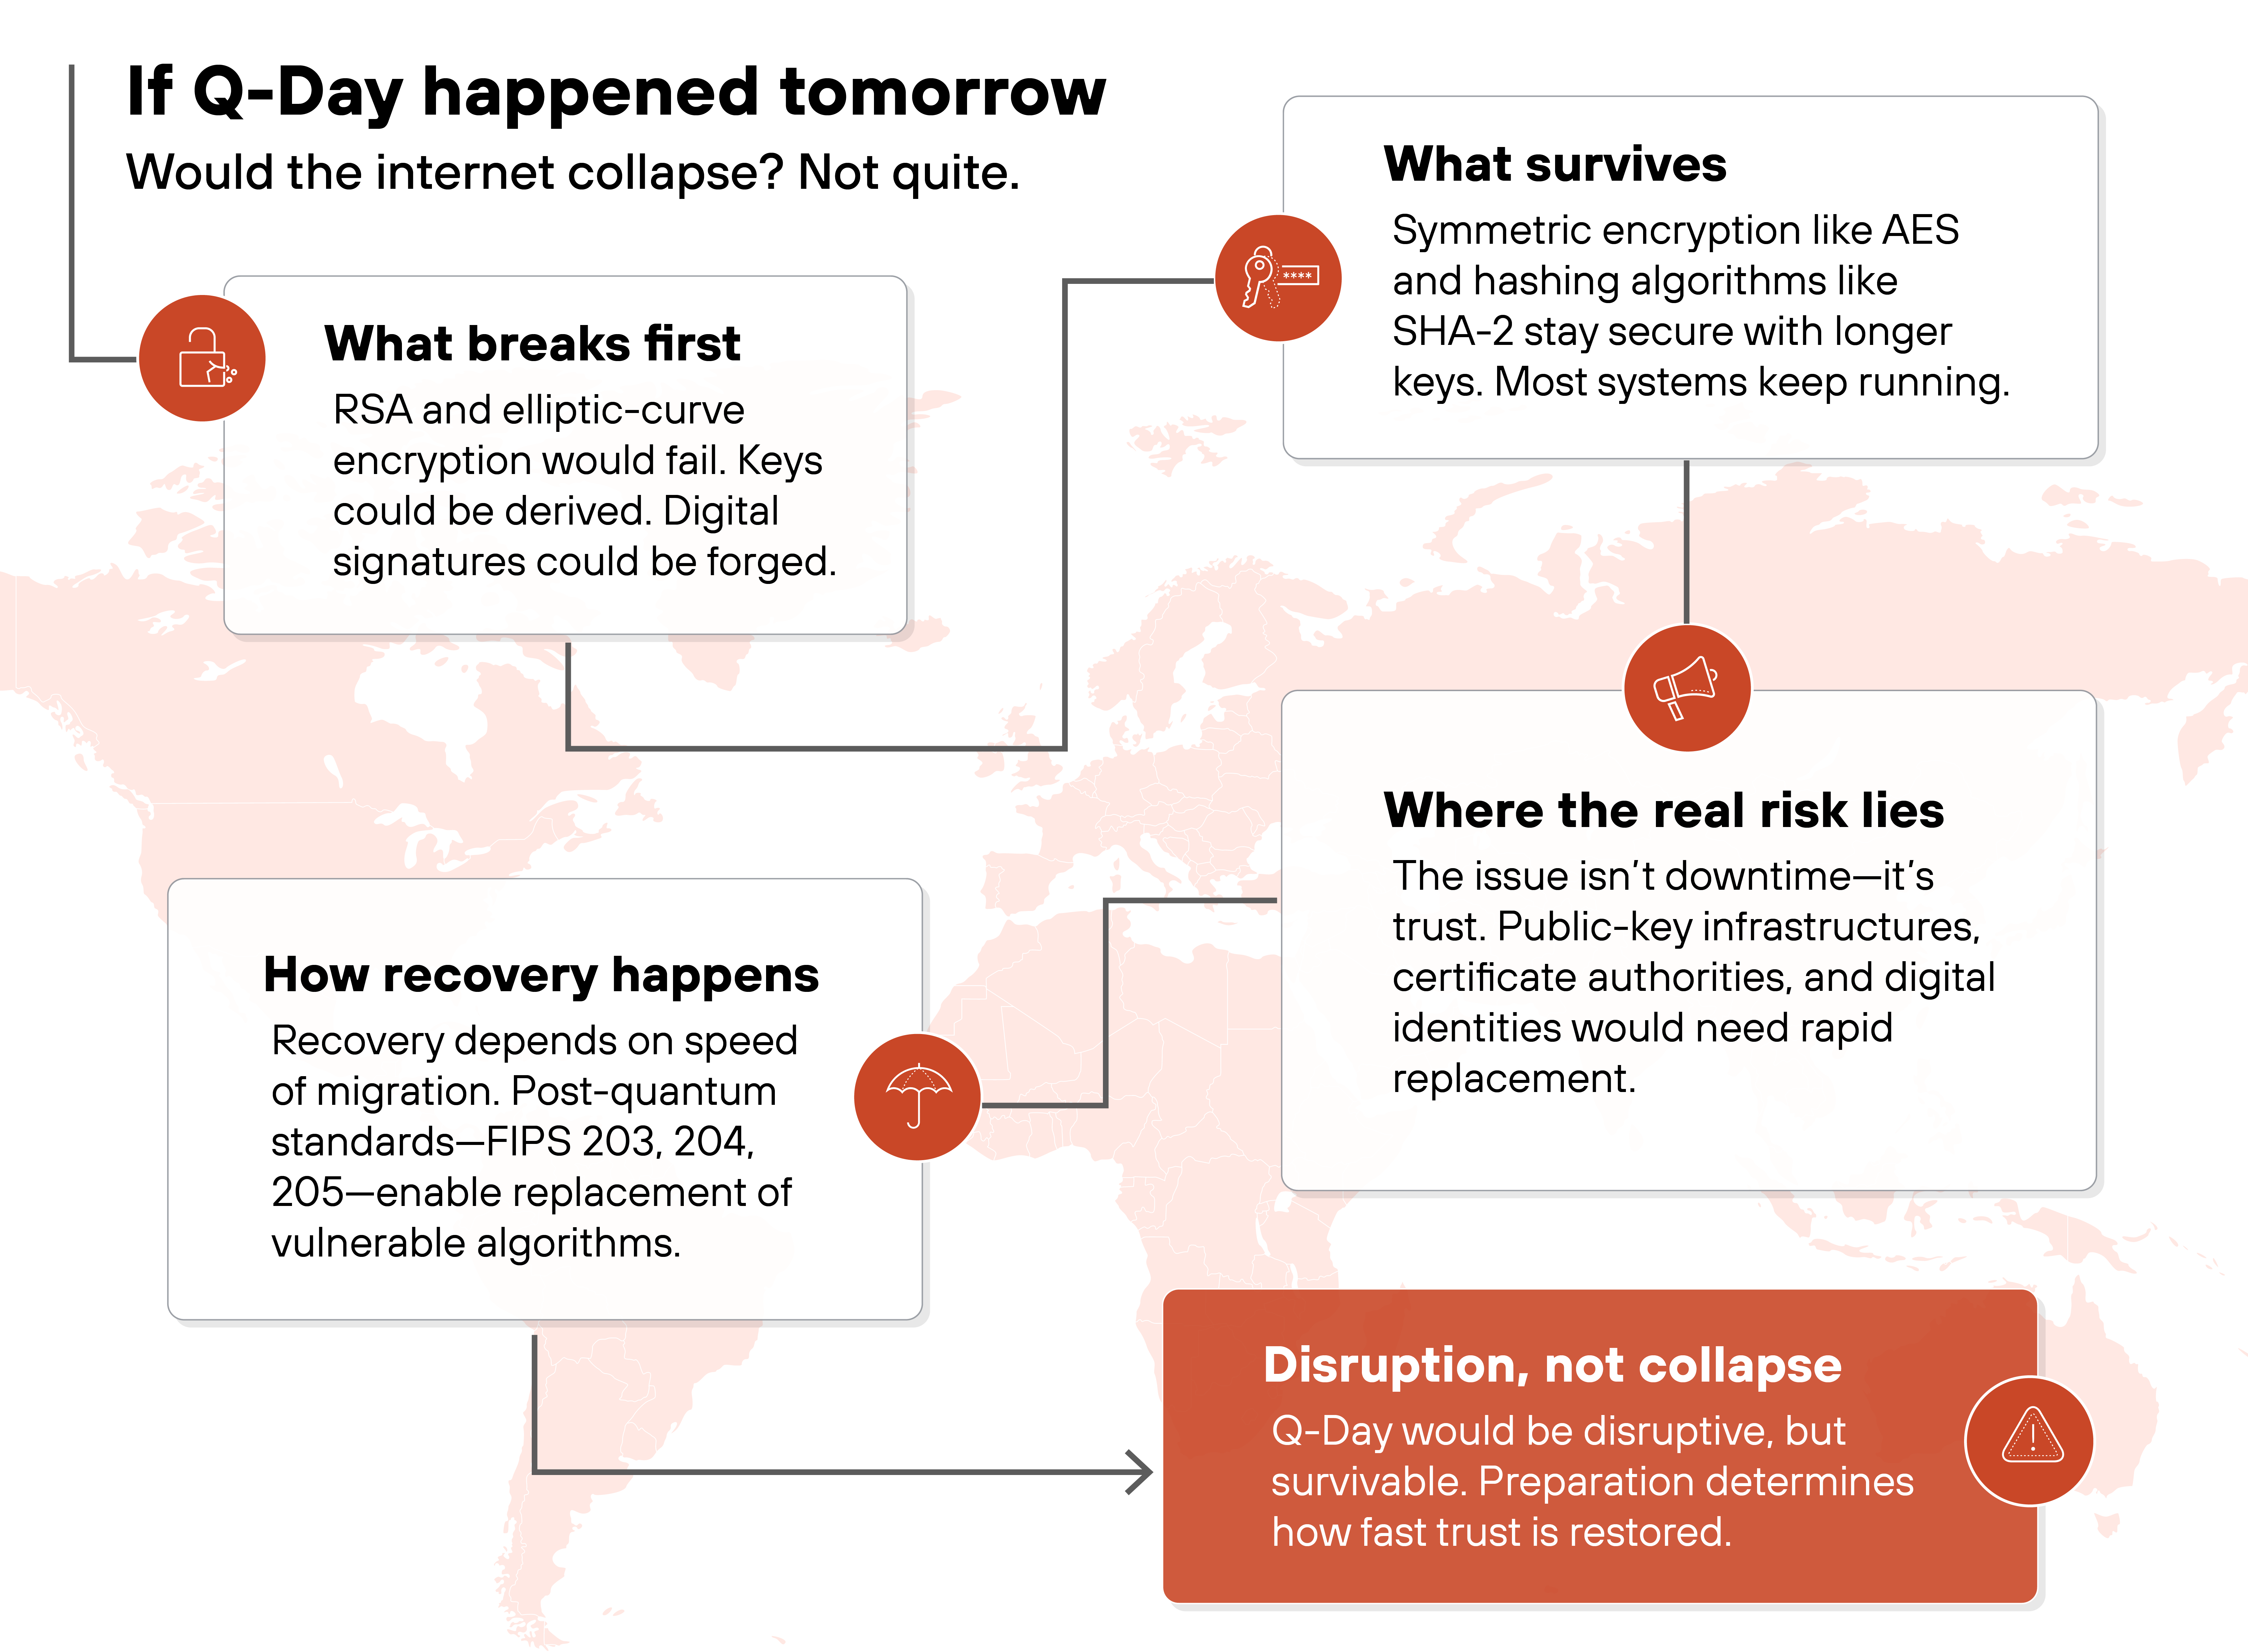
If Q-Day happened tomorrow, the internet would not simply go dark. But encryption based on RSA and elliptic-curve cryptography would no longer be trusted.
A CRQC could solve the mathematical problems that today’s public-key algorithms rely on. That means attackers could derive private keys, decrypt protected data, and forge digital signatures.
The first systems at risk would be those using older, static, or poorly managed keys. Systems protecting long-lived sensitive data would be especially exposed, including financial archives, intellectual property, government records, healthcare data, and confidential communications.
However, Q-Day would not instantly break all forms of encryption.
Symmetric encryption and hashing algorithms, such as AES and SHA-2, would remain more resilient when configured with appropriate key lengths. Many systems could continue operating, but the trust layer of the internet would be under pressure.
The largest issue would be verification.
Public key infrastructure, certificate authorities, digital certificates, signing systems, identity systems, and secure communications would need rapid migration to post-quantum cryptographic standards.
In short: Q-Day would cause disruption, not collapse. The severity would depend on how prepared organizations are to replace vulnerable algorithms, rotate keys, update certificates, and deploy quantum-resistant cryptography.
Recommended Reading: 8 Quantum Computing Cybersecurity Risks [+ Protection Tips]
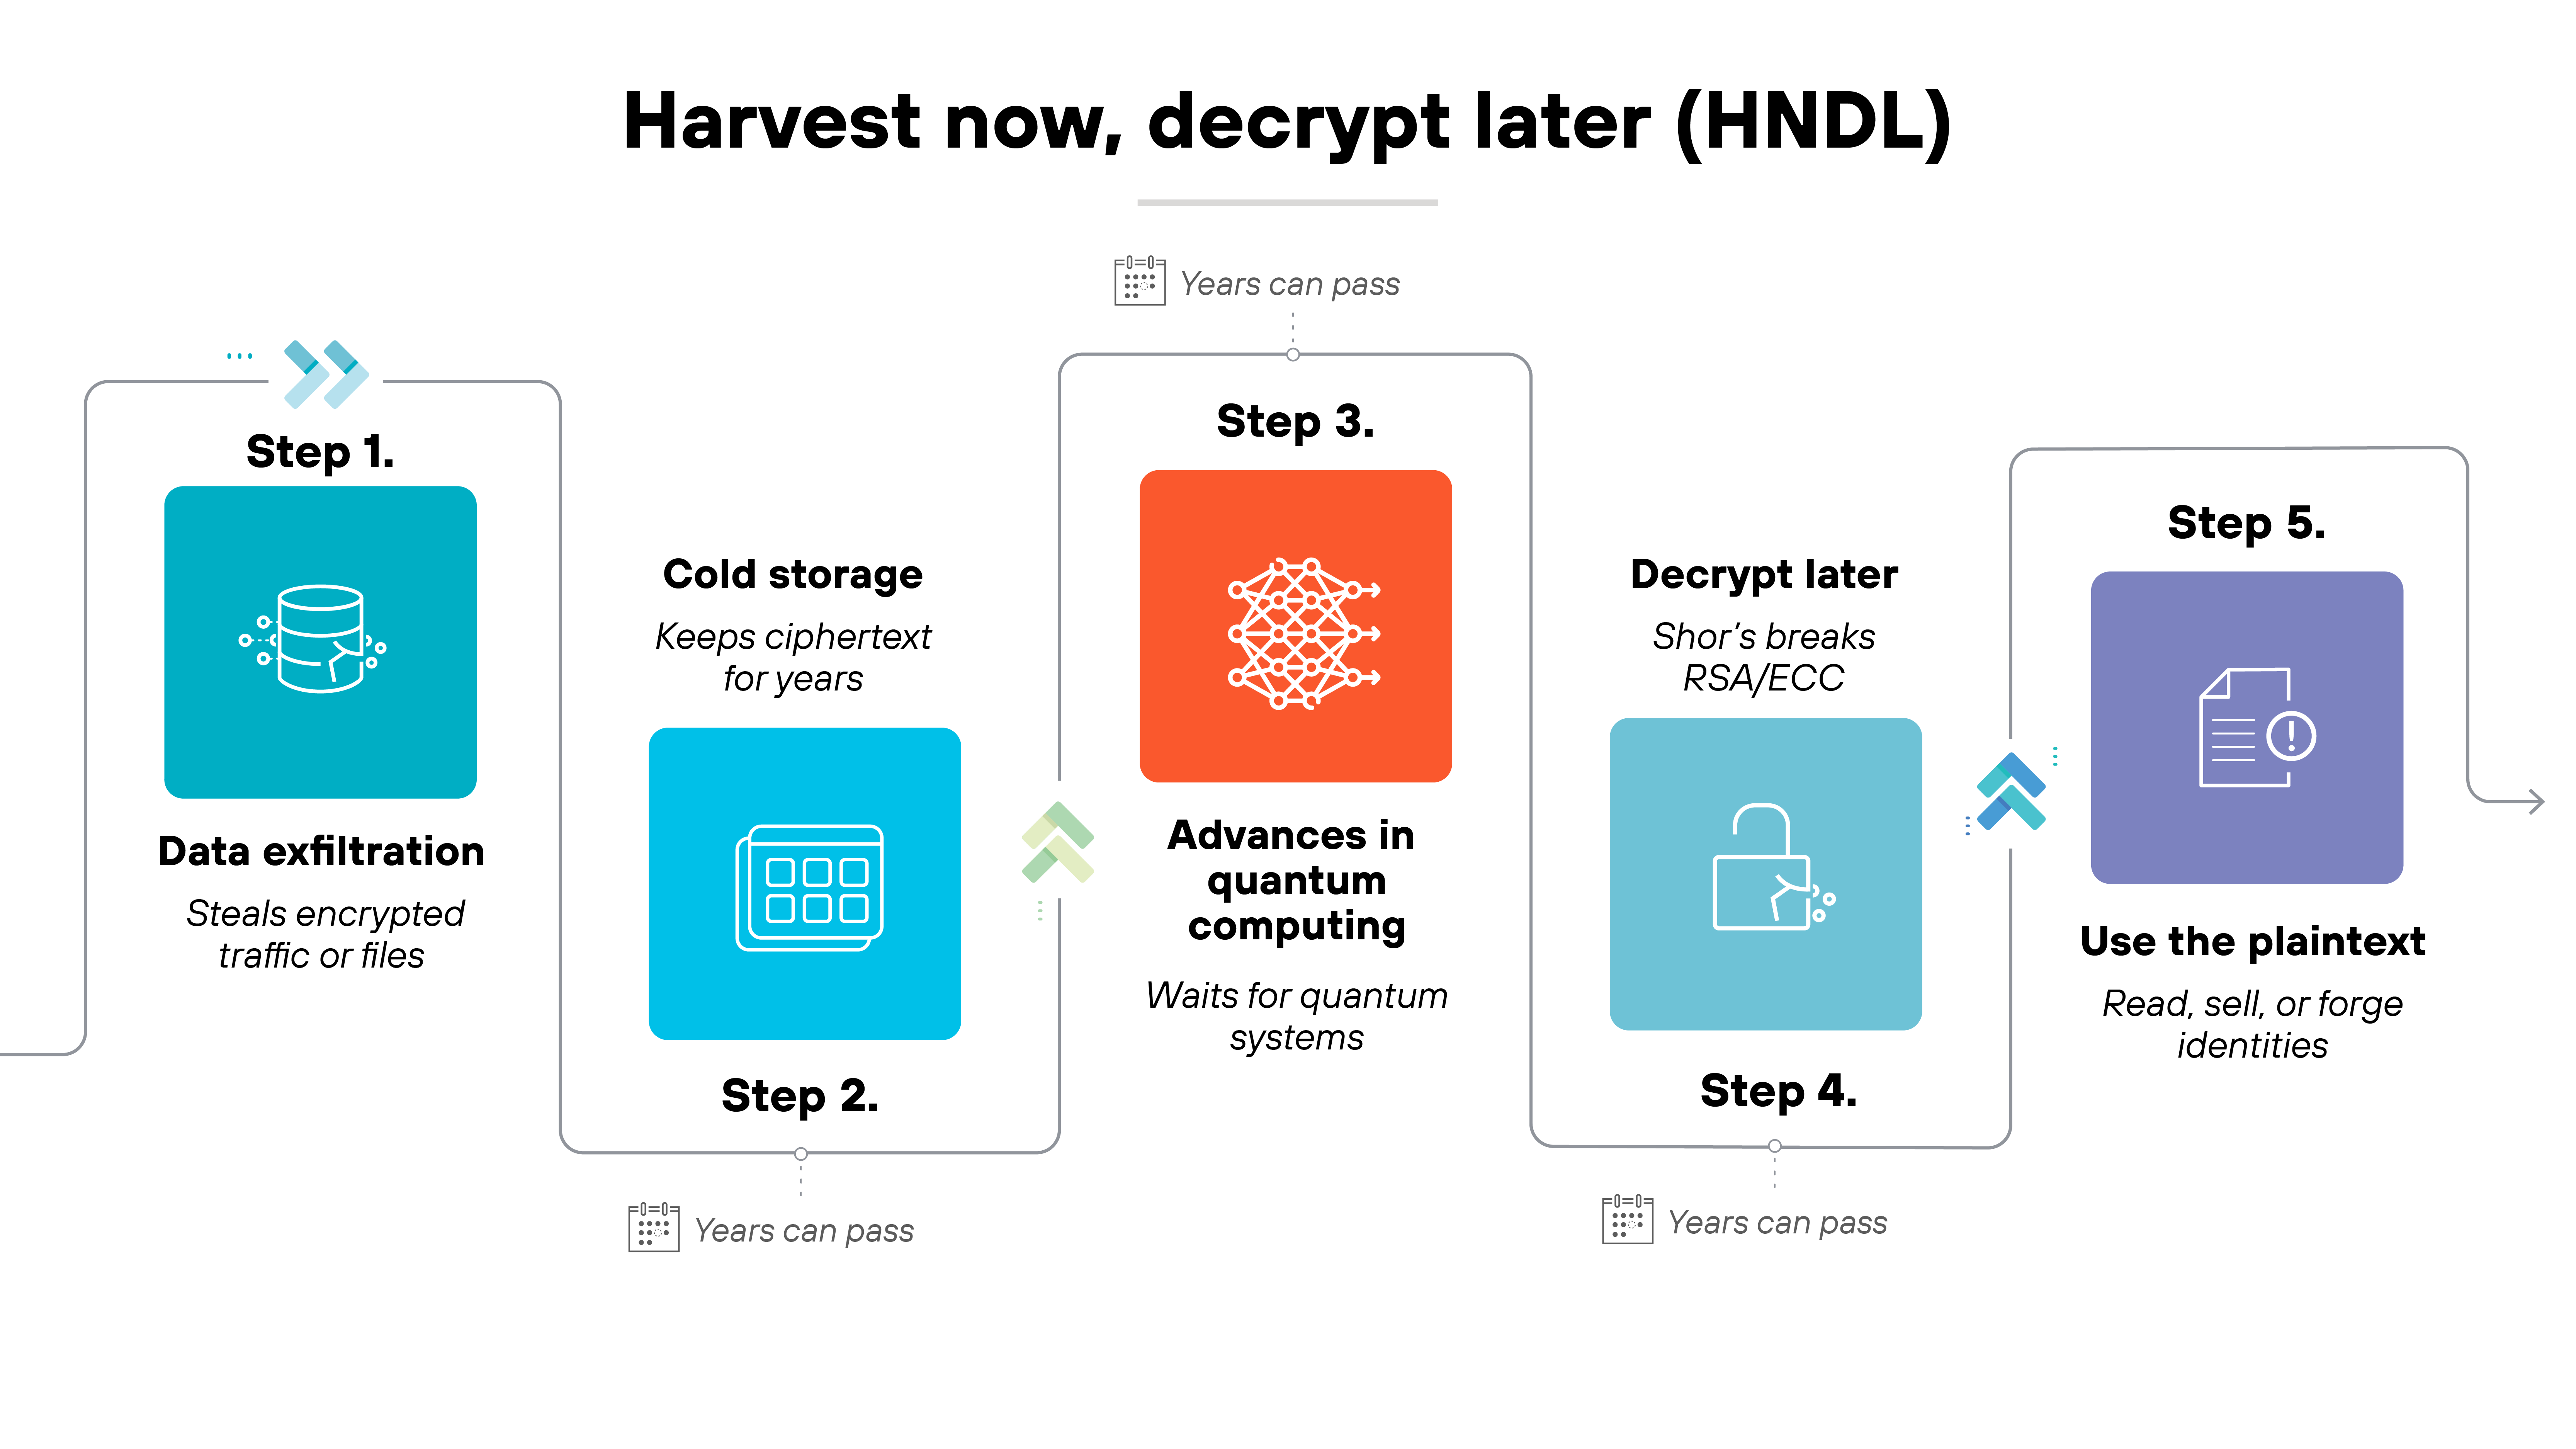
Why Harvest-Now, Decrypt-Later Matters More Than Q-Day Itself
The biggest quantum security threat is not only what happens on Q-Day. It is what attackers can do before Q-Day arrives.
Harvest-now, decrypt-later is a threat model in which attackers steal encrypted data today and store it until quantum computers can decrypt it in the future. This creates immediate risk for data that must remain confidential for many years.
Examples include:
- Government records
- Defense and intelligence data
- Financial records
- Healthcare information
- Legal documents
- Trade secrets
- Product designs
- Research data
- Long-term identity records
The longer the confidentiality lifespan of the data, the greater the exposure.
This is why quantum readiness cannot wait until quantum computers are fully mature. Organizations need to protect sensitive data now so it remains secure later.
Unit 42 Perspective: Q-Day Risk Starts With Today’s Data Theft
Unit 42 insight: Q-Day is not only about future decryption capability. It is also about the sensitive data that adversaries can collect before that capability exists.
Q-Day is a future cryptographic milestone, but the exposure begins with present-day data theft. Unit 42’s 2026 Global Incident Response Report found that the fastest quartile of intrusions reached data exfiltration in 72 minutes in 2025, a sharp decrease from 285 minutes in 2024.
For security teams, this means Q-Day preparation cannot wait for quantum computers to mature. Sensitive encrypted data may already be leaving environments during fast-moving intrusions. If that data has a long confidentiality lifespan, it may remain valuable when cryptographically relevant quantum computers become available.
Unit 42 also reports that 87% of attacks unfolded across multiple attack surfaces, which reinforces the need for quantum readiness planning across endpoints, cloud, SaaS, identity, and network environments.
How Close Are We to Q-Day?
Q-Day is not imminent, but it is no longer theoretical.
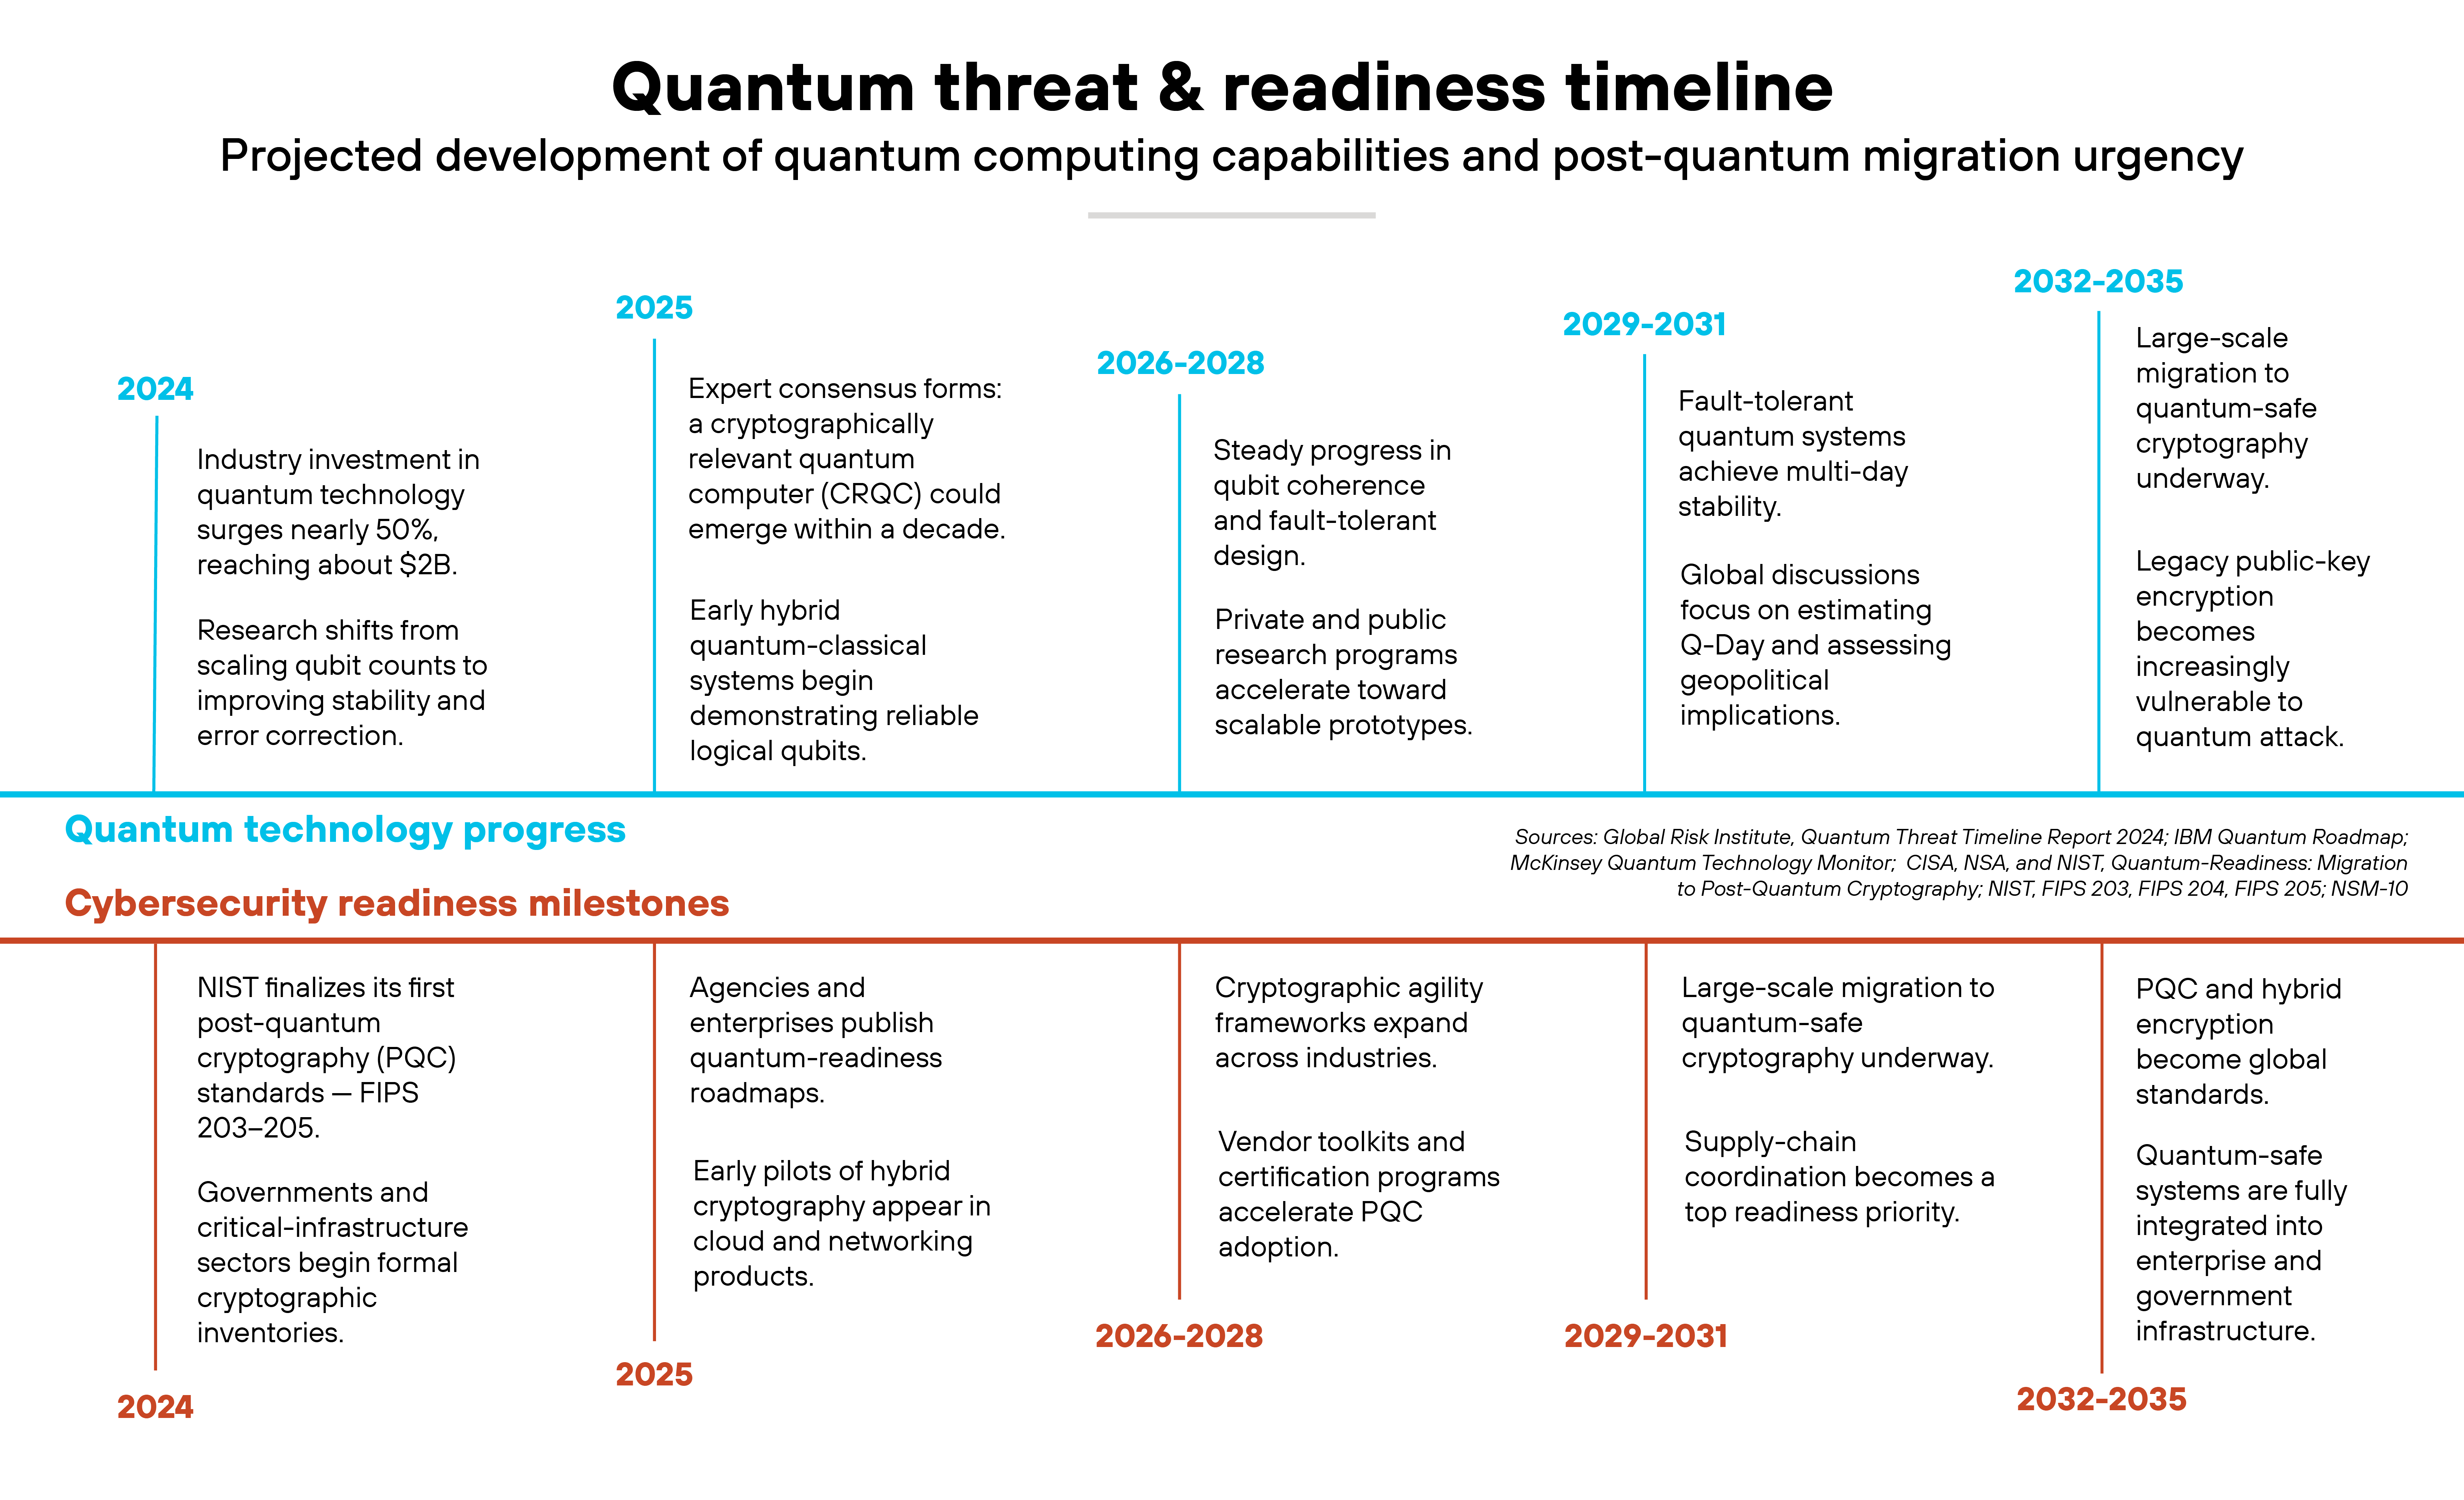
Most current expert assessments suggest that cryptographically relevant quantum computers are still years away, likely arriving in the 2030s or later. The challenge is not simply building more qubits. Quantum systems must also become stable, fault-tolerant, and capable of running long cryptographic attacks reliably.
Current quantum systems have made measurable progress in qubit quality, stability, and error correction. But they remain far from the scale needed to break RSA or elliptic-curve cryptography in real-world conditions.
At the same time, migration planning is already underway.
NIST finalized its first post-quantum cryptography standards in 2024:
- FIPS 203: Module-Lattice-Based Key-Encapsulation Mechanism, or ML-KEM
- FIPS 204: Module-Lattice-Based Digital Signature Standard, or ML-DSA
- FIPS 205: Stateless Hash-Based Digital Signature Standard, or SLH-DSA
These standards give governments, vendors, and enterprises a clearer path toward quantum-resistant cryptography.
The takeaway is straightforward: Q-Day is not expected tomorrow, but the migration window is already open.
Organizations that begin now will have time to inventory cryptography, assess risk, test post-quantum algorithms, coordinate with vendors, and migrate safely. Organizations that wait may face compressed timelines and higher exposure.
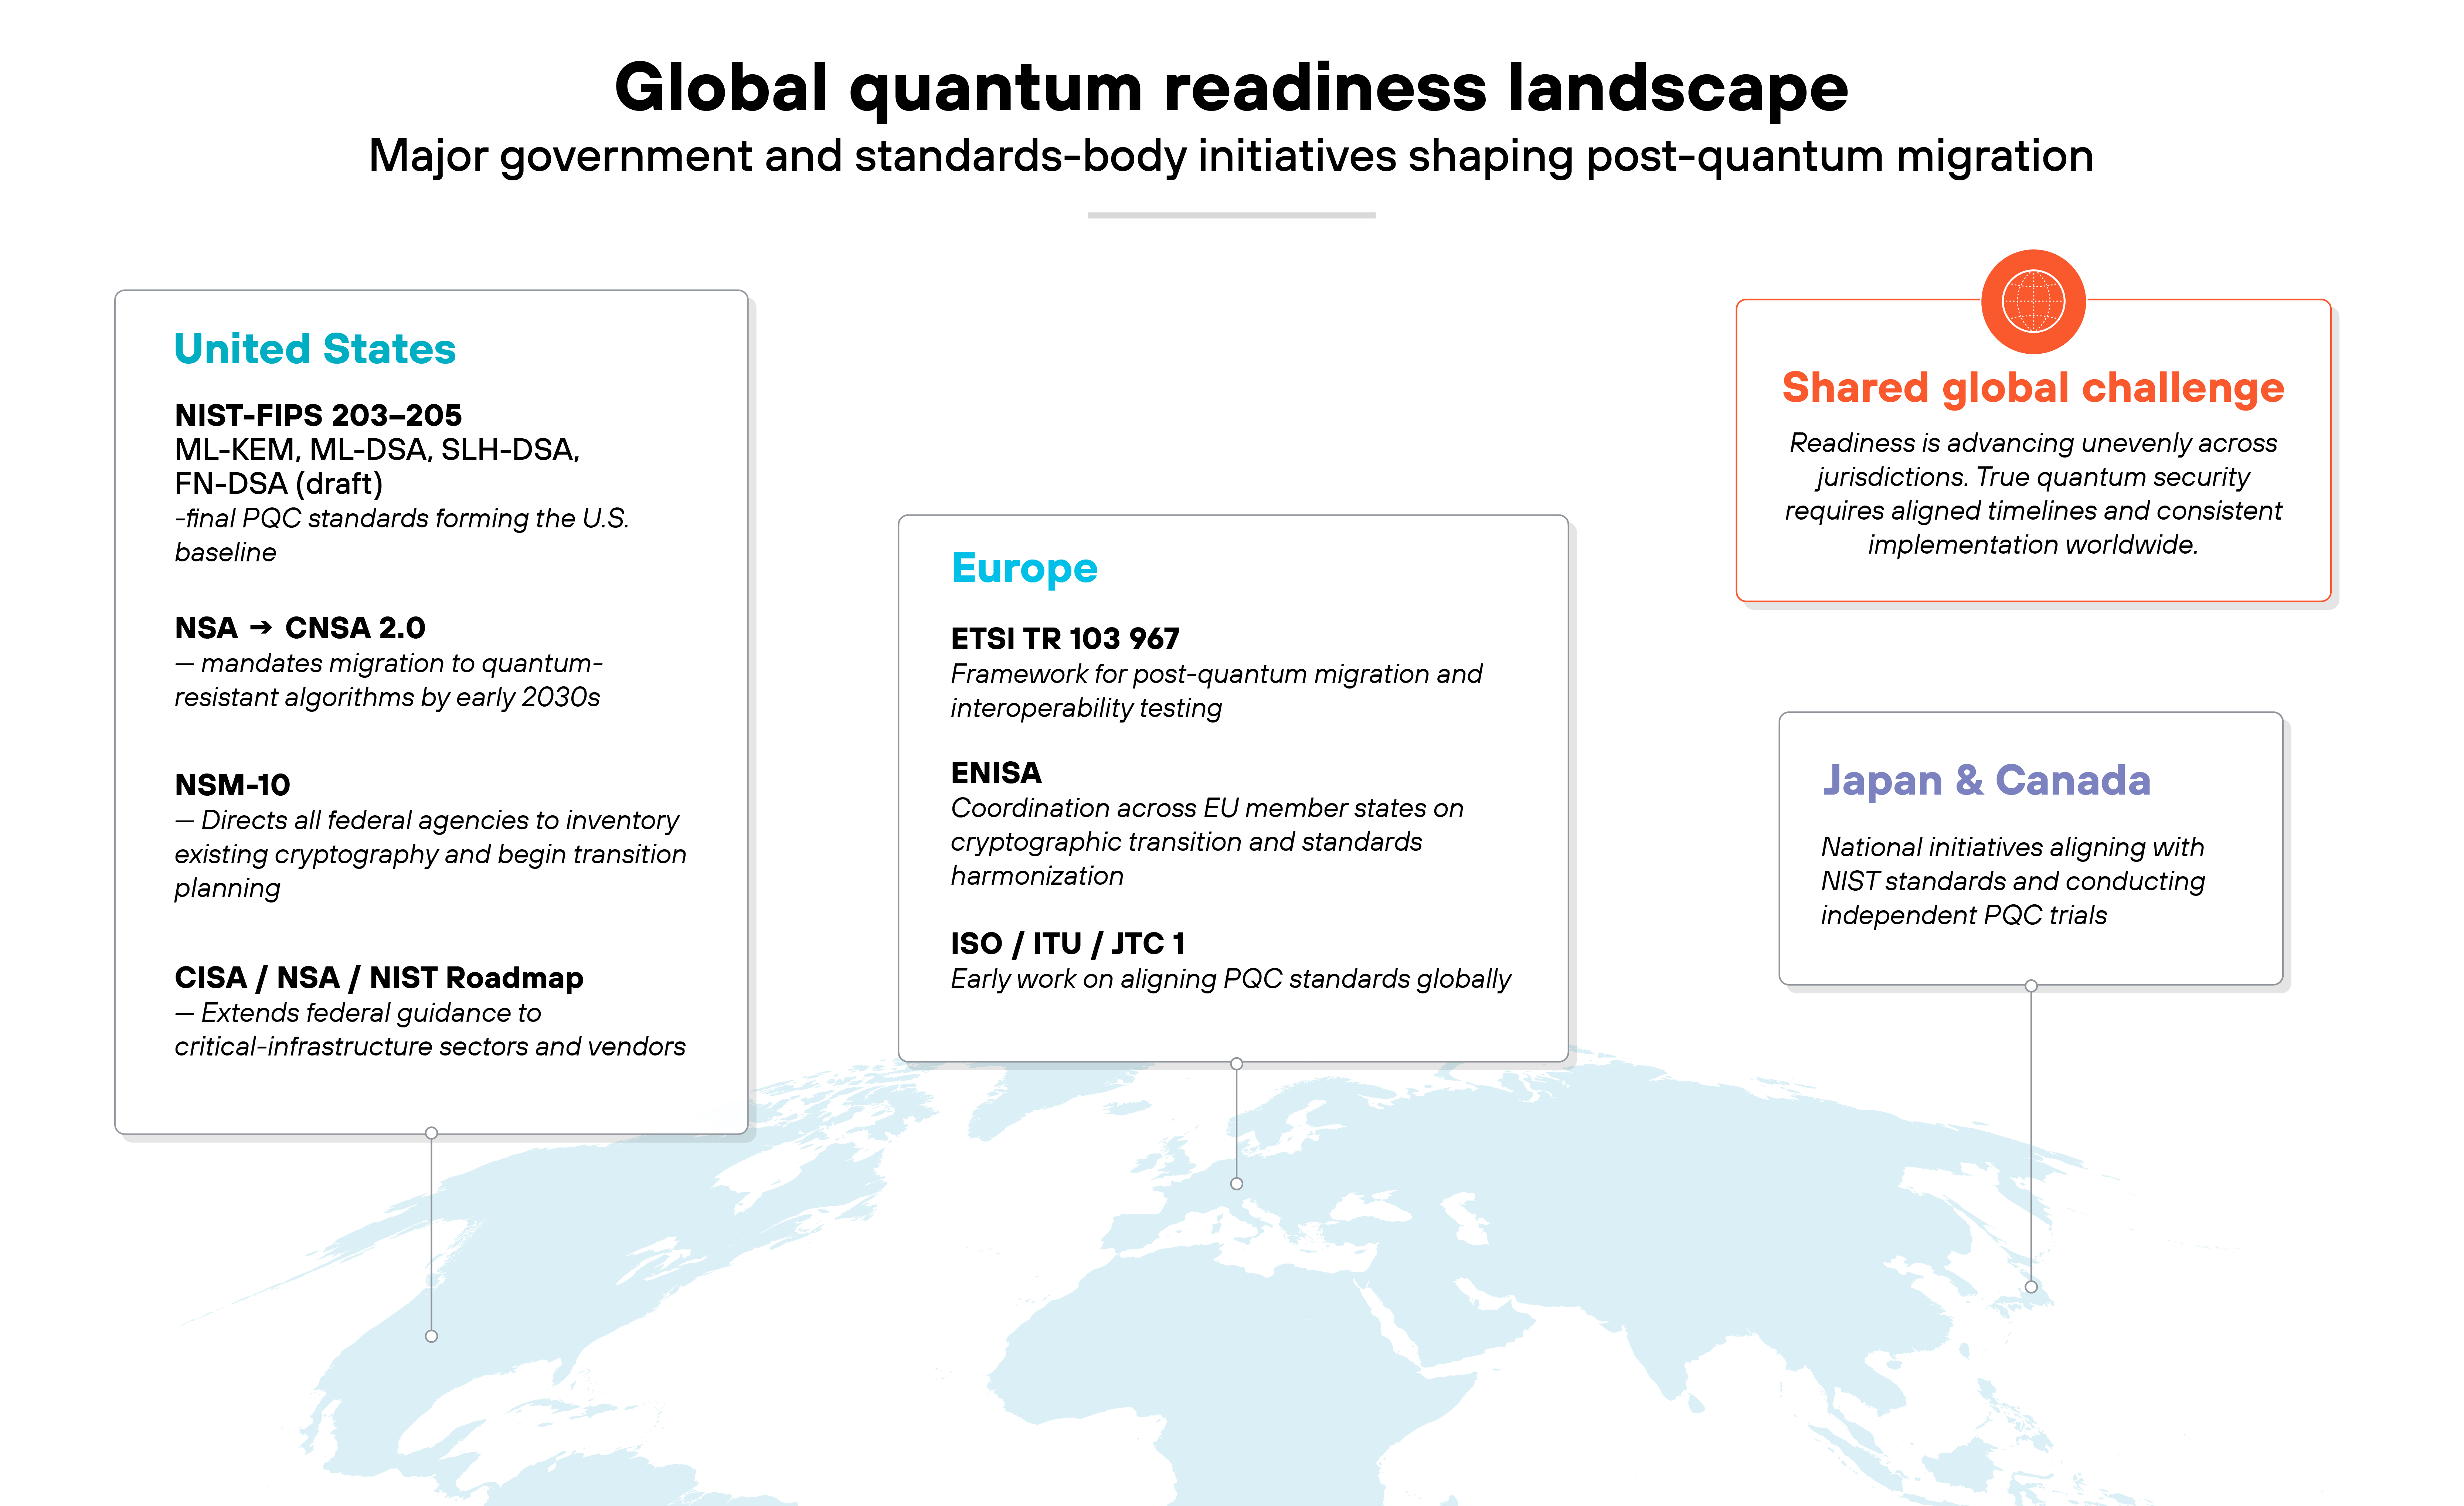
What Are Governments and Standards Bodies Doing to Prepare?
Governments and standards bodies are moving from research to implementation.
In the United States, NIST PQC standards establish approved algorithms for quantum-resistant key encapsulation and digital signatures.
Federal policy is also accelerating migration. U.S. agencies have been directed to inventory cryptographic systems, assess quantum risk, and prepare migration plans for post-quantum cryptography.
The NSA’s Commercial National Security Algorithm Suite 2.0, or CNSA 2.0, also provides guidance for national security systems transitioning to quantum-resistant algorithms.
Globally, organizations such as ENISA, ETSI, ISO, and other standards bodies are developing guidance for post-quantum migration, interoperability, testing, and implementation.
The direction is clear: Global standards are converging, migration timelines are emerging, and organizations are expected to begin planning now.
How to Prepare for Q-Day Without Overreacting
"A successful post-quantum cryptography migration will take time to plan and conduct. CISA, NSA, and NIST urge organizations to begin preparing now by creating quantum-readiness roadmaps, conducting inventories, applying risk assessments and analysis, and engaging vendors. Early planning is necessary as cyber threat actors could be targeting data today that would still require protection in the future (or in other words, has a long secrecy lifetime), using a catch now, break later or harvest now, decrypt later operation."
- NIST, NSA, CISA, Quantum-Readiness: Migration to Post-Quantum Cryptography
Preparing for Q-Day is not about panic. It is about disciplined security planning.
Organizations should begin with leadership, visibility, prioritization, testing, and governance.
1. Assign Ownership
Quantum readiness needs executive and technical ownership. Security leaders should define who is responsible for cryptographic risk, PQC migration planning, and progress reporting.
2. Build a Cryptographic Inventory
Organizations need to know where cryptography is used across applications, APIs, certificates, keys, cloud services, devices, infrastructure, and third-party systems.
Without this inventory, teams cannot prioritize migration or understand their true exposure.
3. Prioritize Long-Lived Sensitive Data
Data with a long confidentiality lifespan should be prioritized first. This includes information that would still be valuable or damaging if exposed 10, 20, or 30 years from now.
4. Assess Vendor Readiness
Many cryptographic dependencies exist in vendor-managed products and services. Procurement and security teams should ask vendors about their post-quantum roadmaps, crypto-agility, and support for NIST PQC standards.
5. Test Post-Quantum Cryptography
Organizations should pilot post-quantum and hybrid cryptographic approaches in controlled environments before broad deployment. Testing helps identify performance, interoperability, latency, and operational challenges.
6. Build Crypto-Agility
Crypto-agility is the ability to replace cryptographic algorithms, keys, certificates, and protocols without redesigning entire systems. It is one of the most important long-term capabilities for quantum readiness.
7. Create a Quantum Readiness Roadmap
A readiness roadmap should define owners, milestones, dependencies, technical priorities, vendor requirements, and migration timelines. The objective is not to replace every cryptographic system overnight. The objective is to make migration manageable before it becomes urgent.
Will Q-Day Be a Crisis or a Milestone?
Q-Day will not be a single moment when the internet collapses. It will be a milestone that reveals how well organizations are prepared.
Systems built with cryptographic visibility, crypto-agility, and post-quantum migration plans will be better positioned to adapt. Systems that rely on unknown cryptographic dependencies, legacy algorithms, and static keys will face greater disruption.
The transition to quantum-safe security is already underway. Standards exist. Timelines are emerging. Vendor roadmaps are being developed. The real challenge is execution.
Q-Day is not a surprise waiting to happen. It is a predictable security milestone. Whether it becomes a crisis depends on whether organizations start preparing now.

Explore the future of quantum security
Dive into an interactive overview of quantum threats, post-quantum cryptography, and NIST's new standards.Q-Day FAQs
Q-Day refers to the point when quantum computers become powerful enough to break widely used public-key cryptography, such as RSA and elliptic-curve cryptography. It is a capability milestone, not a specific calendar date.
Most experts expect Q-Day to occur in the 2030s or later, but no one can predict the exact date. The timing depends on advances in quantum hardware, error correction, algorithm design, and fault-tolerant computing.
Q-Day is a cybersecurity risk because many systems rely on public-key cryptography to secure communications, authenticate users, verify software, and protect digital trust. A cryptographically relevant quantum computer could break those protections.
A cryptographically relevant quantum computer is a quantum computer powerful and reliable enough to break widely used cryptographic algorithms, such as RSA and elliptic-curve cryptography, in practical timeframes.
Harvest-now, decrypt-later is a threat model in which attackers steal encrypted data today and store it until quantum computers can decrypt it in the future. It creates immediate risk for sensitive data that must remain confidential for many years.
Yes. Organizations can prepare by building cryptographic inventories, prioritizing high-risk systems, adopting post-quantum cryptography, testing hybrid approaches, engaging vendors, and building crypto-agility into their architectures.
No. Q-Day would not instantly break the entire internet. It would primarily threaten public-key cryptography, digital signatures, certificates, and identity systems. The level of disruption would depend on how prepared organizations are to migrate to quantum-resistant algorithms.
The first step is to identify where cryptography is used. A cryptographic inventory helps organizations understand which systems, applications, certificates, keys, and vendors depend on quantum-vulnerable algorithms.


